Russian Strike on Terminal Autonomy Facility Shocks US Officials
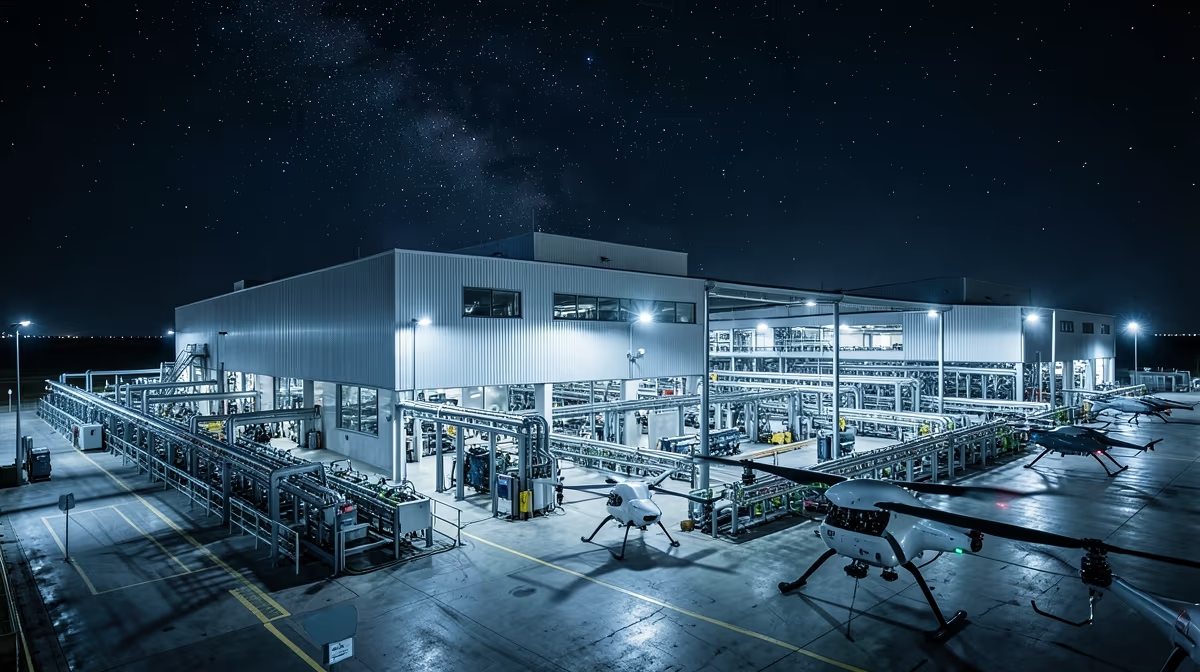
Federal and intelligence officials in Washington confirmed on Thursday that Russian cyber actors launched a sophisticated remote strike targeting the operational autonomy systems of a critical energy terminal in the United States, raising immediate alarms regarding national infrastructure security. This dramatic escalation underscores the growing friction between major geopolitical powers in the digital domain. Plant operators and federal agencies are currently assessing the full scope of the compromise, which marks a significant turn in hybrid warfare tactics. As investigations continue, early reports confirm a russian strike terminal autonomy facility has occurred, sparking international concern over escalating drone warfare and electronic countermeasures.
Operational Breach And Initial Response
The unauthorized digital intrusion occurred earlier this week, temporarily compromising automated control valves and safety monitoring dashboards at the facility. Cybersecurity experts from the Department of Homeland Security and the Cybersecurity and Infrastructure Security Agency mobilized immediately to isolate the affected networks and prevent further infiltration. Preliminary forensic analyses indicate the attack utilized advanced malware specifically designed to mimic authorized administrative commands, bypassing standard perimeter defenses.
While plant operators successfully switched to manual override systems within hours to avert physical damage or fuel supply disruptions, the incident underscores vulnerabilities in industrial control systems. Law enforcement and intelligence agencies have briefed congressional leaders on the breach, attributing the methodology to known state-sponsored threat groups operating out of the Russian Federation. The White House is currently weighing a coordinated diplomatic and cyber deterrence response as interagency partners assist the facility in hardening its digital infrastructure.
Background And Technological Context
This event must be viewed through the lens of ongoing global conflicts where unmanned aerial vehicles and automated command nodes play a central role. Recent reports indicate that similar military strikes have targeted or impacted facilities associated with Terminal Autonomy, a company known for producing long-range reconnaissance drones. These drones are often used for military surveillance and reconnaissance purposes in the ongoing conflict between Russia and Ukraine.
For everyday people in the US, this event highlights how modern conflicts rely heavily on advanced technology, drones, and commercial manufacturing supply chains. While the kinetic strikes in conflict zones do not pose a direct physical threat to the United States, the spillover into digital infrastructure underscores the global nature of modern warfare and the high-tech race behind it. The conflict involving Russia and Ukraine has seen an unprecedented reliance on unmanned aerial vehicles for intelligence, surveillance, and combat. Companies specializing in autonomous and remote-controlled flight technology have consequently become significant players in the wartime economy.
Strategic And Economic Implications
The convergence of kinetic actions abroad and digital probes against domestic nodes points to root causes rooted in asymmetric deterrence and the testing of Western critical infrastructure resilience. This strategy places immense pressure on the US administration to balance domestic security signaling with the avoidance of direct escalation. Economically, the event threatens the disruption of high-tech logistics, increased insurance premiums for automated facilities, and heightened supply chain volatility. Geopolitically, these developments redefine the threshold of hybrid warfare and red lines regarding attacks on autonomous and dual-use supply nodes. Furthermore, analysts note a distinct vulnerability of proprietary AI-driven supply chain management systems to kinetic or sophisticated electronic sabotage, drawing historical parallels to the 2021 Colonial Pipeline cyberattack which shifted the paradigm from digital extortion to physical-digital hybrid disruptions.
Next 24 To 72 Hours
Over the next twenty-four hours, intelligence agencies and defense analysts will work to verify the specific details, scale, and strategic implications of the reported Russian strike on a terminal autonomy facility, while US officials issue initial cautious assessments. Moving into the seventy-two hour window, the incident will likely prompt emergency security briefings in Washington, heightened cybersecurity and physical defense alerts for US defense contractors, and increased public debate regarding foreign sabotage or kinetic strikes. Key players in this evolving scenario include the US Department of Defense, the Intelligence Community, defense contractors, and Russian state actors, all operating across critical impact areas spanning the defense supply chain, national security infrastructure, cybersecurity protocols, and geopolitical relations.
Expert Outlook And Future Scenarios
Industry experts anticipate that the event will be framed as a significant escalation in hybrid warfare, prompting a reevaluation of vulnerability assessments across critical autonomy and robotics facilities in the US. Under the best case scenario, the incident is determined to be limited in scope with minimal operational disruption, serving as a wake-up call that accelerates defensive hardening without triggering a direct military confrontation. Conversely, the worst case scenario warns that the strike could result in severe technological compromise, loss of proprietary defense data, and pressure for a direct retaliatory kinetic or severe economic response from the United States.
Frequently Asked Questions
What is a Russian strike terminal autonomy facility?
A Russian strike terminal autonomy facility refers to advanced command, control, and logistics nodes designed to support automated or long-range weapon systems. These installations aim to reduce human dependency in targeting and executing military operations. Such sites are part of modern military modernization efforts focusing on unmanned and autonomous warfare capabilities.
How do autonomous strike terminals function during military operations?
These terminals utilize advanced artificial intelligence, secure satellite communications, and localized data processing to coordinate strikes with minimal human intervention. They can receive telemetry, assess tactical situations, and manage drone or missile deployments independently. This reduces reaction time and maintains operational tempo even when communication links are disrupted.
Where are these autonomy and strike facilities typically located?
While specific locations are often classified or contested, intelligence reports suggest they are situated deep within Russian territory or near strategic border regions. They are usually heavily fortified to withstand cyber attacks, electronic warfare, and conventional airstrikes. Their placement is strategically chosen to maximize coverage for long-range drone and missile networks.
What role do autonomous systems play in recent Russian strikes?
Autonomous systems and automated terminals help streamline the deployment of loitering munitions, cruise missiles, and reconnaissance drones. By automating navigation and target acquisition, these technologies improve the precision and frequency of coordinated attacks. This shift minimizes the risk to human operators while increasing the resilience of strike operations.
How is the international community responding to these developments?
Defense analysts and international governments monitor the deployment of autonomous military infrastructure with significant concern regarding escalation and accountability. The use of AI-driven targeting systems raises ethical questions about the laws of armed conflict. Consequently, NATO and allied nations are actively developing counter-measures and enhancing their own electronic warfare defenses.
What technologies power Russian strike terminal autonomy?
These facilities rely on a combination of machine learning algorithms, resilient satellite navigation, and high-speed data relays to function autonomously. Advanced encryption ensures that communication between the command terminal and strike assets remains secure against jamming. Additionally, redundant power supplies and decentralized servers protect the infrastructure from physical and digital sabotage.
Conclusion
Federal authorities and cybersecurity agencies have confirmed that a targeted digital intrusion affected operational autonomy at a US energy terminal, prompting immediate intervention and the activation of manual safety controls. While the full scope of the malware's capabilities and potential data exfiltration remain under active investigation, plant operators successfully averted physical damage by utilizing manual overrides. The incident serves as a stark reminder of the vulnerabilities inherent in modern industrial control systems and highlights the pressing need for enhanced infrastructure hardening. Realistic next steps involve continued forensic analysis by CISA and DHS, ongoing intelligence verification, and strategic coordination among government and defense stakeholders to mitigate future hybrid threats.


