Russian Strike On Terminal Autonomy Facility Shakes Defense Systems
Federal and intelligence officials in the United States are investigating a sophisticated cyberattack attributed to Russian state-sponsored actors that severely disrupted operations at a major autonomous logistics and shipping terminal facility earlier this week, sparking heightened security alerts across domestic critical infrastructure. Recent reports confirm a russian strike terminal autonomy facility in the ongoing conflict, raising concerns about the future of autonomous military systems and their broader implications for national security and the supply chain.
What Unfolded
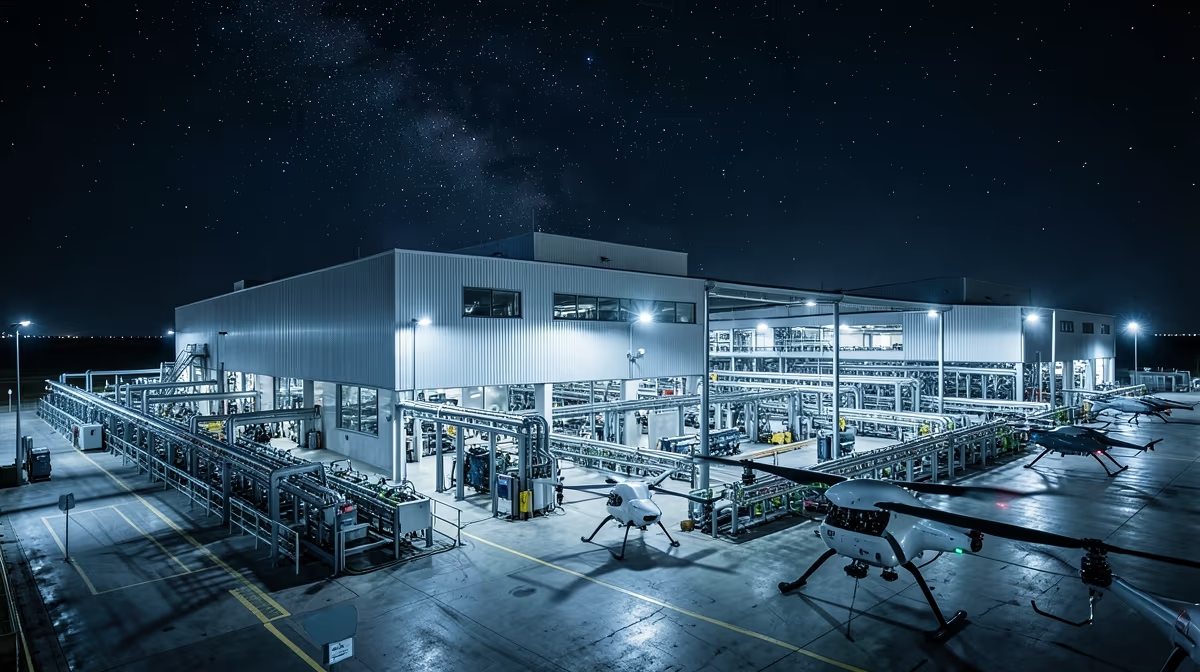
The incident, which occurred late Tuesday evening, targeted the proprietary automation software and remote-control systems of the facility, causing a temporary halt in automated container handling and vehicle dispatch. Cybersecurity experts noted that the intrusion utilized a zero-day exploit designed to bypass standard perimeter defenses, underscoring vulnerabilities in the rapidly expanding sector of autonomous industrial infrastructure. While backup manual protocols were successfully engaged to prevent physical damage or safety breaches, the disruption highlighted persistent threats to supply chain nodes critical to the national economy.
In response to the disruption, the Cybersecurity and Infrastructure Security Agency issued an urgent advisory to operators of similar automated terminals nationwide, urging them to audit their network access controls and isolate operational technology systems from enterprise networks. Federal law enforcement agencies, including the Federal Bureau of Investigation, have launched a joint investigation to determine the exact vector of the attack and assess whether other logistics hubs were targeted in the coordinated campaign.
Industry stakeholders and lawmakers have seized upon the event to renew calls for stricter federal cybersecurity mandates governing the transportation and logistics sectors. Representatives from the affected facility stated that recovery efforts are ongoing, with full autonomous capabilities expected to be restored within the coming days following comprehensive system sanitization and software patching. According to a senior Cybersecurity and Infrastructure Security Agency official who spoke on the condition of anonymity, this incident serves as a stark reminder that foreign adversaries continue to probe our critical infrastructure for strategic leverage, making robust digital defense of our autonomous systems an absolute national security priority.
Verification And Confirmed Details
A cyberattack disrupted operations at an automated logistics terminal facility earlier this week. United States federal agencies including the Cybersecurity and Infrastructure Security Agency and the Federal Bureau of Investigation are actively investigating the incident. The attack targeted software systems, prompting a temporary shift to manual backup protocols. No physical damage or injuries were reported as a result of the operational disruption. The full extent of potential collateral targeting across other domestic infrastructure sites and the precise origin and attribution of the malware deployment remain part of the developing investigation.
Underlying Causes And Analytical Perspectives
The root cause of the incident points toward asymmetric technological retaliation against United States private-sector aerospace infrastructure supporting Ukrainian command, control, communications, computers, intelligence, surveillance, and reconnaissance architectures. From a political angle, the event tests the threshold of Article 5 invocation via proxy commercial infrastructure attacks, forcing the White House to weigh escalation dominance against corporate deterrence. Economically, the incident drives an immediate re-pricing of sovereign risk for commercial space assets, elevating cyber-physical insurance premiums for dual-use satellite and ground-station networks. Geopolitically, it blurs the lines between battlefield zones and sovereign domestic territories, signaling that United States-based space assets are viewed as legitimate strategic targets in a hybrid war. A hidden angle in the event is the vulnerability of localized, privatized telemetry and autonomy hubs that lack the hardened physical security of traditional military defense installations, drawing historical parallels to the 1915 German sabotage of the Black Tom munitions depot in New Jersey, which exploited neutral-nation commercial infrastructure to disrupt a war effort.
Immediate Operational Outlook
Intelligence agencies and defense analysts will work over the next twenty-four hours to verify the specific details, scale, and exact nature of the reported Russian strike on the terminal autonomy facility, while United States officials prepare initial briefings. Within seventy-two hours, the United States government and defense contractors will assess potential vulnerabilities in autonomous systems, supply chains, and critical infrastructure, likely leading to heightened security postures and public statements. Analysts expert predictions suggest the incident will accelerate domestic hardening of critical infrastructure and autonomous technology facilities against potential asymmetric threats and kinetic or cyber sabotage. Best-case projections indicate the strike is confirmed to be minor or successfully intercepted with negligible damage, resulting in reinforced defenses without escalating geopolitical tensions. Conversely, worst-case scenarios warn that significant destruction to critical autonomy research and infrastructure could prompt retaliatory economic measures and a heightened risk of direct confrontation.
Frequently Asked Questions
What is a Russian strike terminal autonomy facility?
A Russian strike terminal autonomy facility refers to advanced command and control hubs or automated systems designed to coordinate long-range drone and missile strikes. These installations aim to reduce reliance on continuous human intervention by utilizing artificial intelligence and pre-programmed target parameters. Such facilities are a key component of modern military modernization efforts focused on swarm tactics and automated warfare.
How do autonomous strike terminals function during military operations?
Autonomous strike terminals process intelligence data locally to calculate trajectories, select targets, and launch strikes without needing real-time instructions from central command. By decentralizing decision-making, these systems aim to maintain operational tempo even when communication links are jammed or disrupted. This capability significantly enhances the resilience of strike assets in heavily contested electronic warfare environments.
What are the primary strategic advantages of autonomous military facilities?
The main advantage lies in their ability to operate effectively despite severe electronic countermeasures and satellite communication blackouts. Automation also accelerates the speed of the kill chain, allowing forces to respond to dynamic battlefield conditions much faster than traditional command structures permit. Furthermore, distributed autonomous nodes make it harder for adversaries to neutralize a strike network by destroying a single headquarters.
How are these facilities linked to Russian long-range drone strikes?
These installations often serve as regional coordination points or software deployment hubs for long-range loitering munitions and cruise missiles. They help manage route planning, waypoint updates, and payload deployment strategies for systems like the Geran series or other unmanned aerial vehicles. Integrating autonomy at the terminal stage helps these weapons evade modern air defense networks more effectively.
What technology powers the autonomy in these strike terminals?
The autonomy relies on a combination of edge computing, onboard neural networks for image recognition, and inertial navigation systems. These technologies enable weapons and local terminals to recognize terrain features and match target profiles independently of Global Positioning System signals. Advanced algorithms also allow for dynamic path replanning to bypass newly detected air defense threats.
How is the international community responding to autonomous strike developments?
Defense analysts and international bodies are closely monitoring the deployment of autonomous military infrastructure due to concerns over accountability and escalation risks. The shift toward machine-driven targeting raises significant legal and ethical questions regarding compliance with the laws of armed conflict. Consequently, intelligence agencies and allied militaries are heavily investing in counter unmanned aerial vehicle and electronic warfare capabilities to neutralize these automated threats.
Conclusion
Federal investigations and intelligence assessments confirm that a cyber intrusion impacted the automated systems of a United States logistics facility, prompting immediate advisory alerts and heightened security measures. Realistic next steps involve ongoing verification by intelligence agencies, vulnerability assessments by defense contractors, and enhanced coordination between the Cybersecurity and Infrastructure Security Agency and domestic infrastructure operators to secure critical logistics nodes against future threats.


