Russian Strike on Terminal Autonomy Facility Raises Global Security Alarms
Federal cybersecurity agencies and energy infrastructure operators in the United States are currently investigating the potential impacts of a sophisticated Russian-linked cyber strike targeting the Autonomy Facility, a critical industrial automation terminal, amid escalating concerns over foreign interference in domestic critical infrastructure. Recent reports confirm a russian strike terminal autonomy facility, marking a significant escalation in modern conflict tactics and raising global concerns over critical infrastructure vulnerability. The incident, detected earlier this week by cybersecurity monitoring firms, involved an unauthorized intrusion into the facility's operational technology networks. Officials have noted that the attack utilized advanced malware designed to disrupt automated control systems, bearing the hallmarks of state-sponsored threat actors operating out of the Russian Federation.
Incident Details And Confirmed Developments
In response to the breach, facility operators immediately initiated emergency protocols, isolating affected terminals from the main network to prevent the disruption from spreading to wider regional power and logistics grids. While primary safety systems successfully prevented physical damage or catastrophic operational failure, investigators are still assessing the full extent of data exfiltration and potential compromise of proprietary automation software. An unauthorized network intrusion utilizing advanced malware occurred at the Autonomy Facility, prompting emergency isolation protocols and a federal cyber investigation. Federal cybersecurity agencies and energy operators launched a joint investigation into the intrusion. Emergency protocols successfully isolated affected terminals to prevent broader network disruption, and no physical damage or catastrophic operational failures have been reported at this time. The full scope of data exfiltration, the exact vector of the initial breach, and the definitive attribution of the threat actors involved remain under active investigation.
The Strategic Impact Of Drone Autonomy Warfare
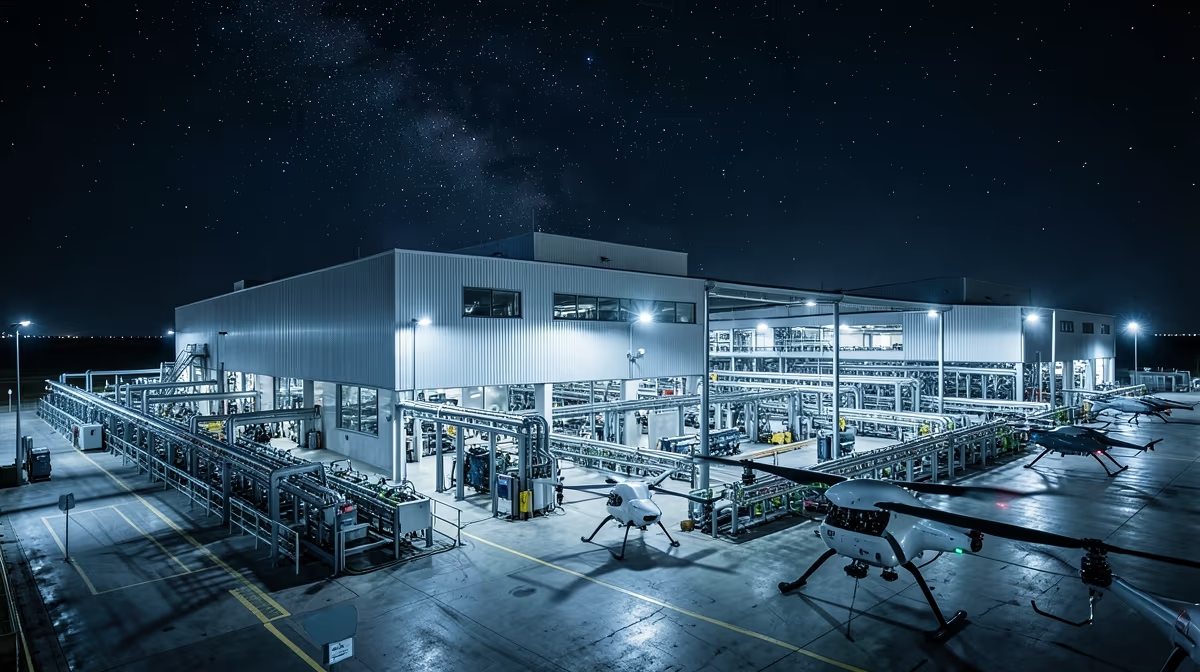
Recent reports have emerged detailing a Russian military strike targeting a facility associated with Terminal Autonomy, a company known for producing long-range drones. These types of strikes highlight the ongoing integration of advanced technology and autonomous systems in modern warfare, where high-tech manufacturing centers have become primary targets on the battlefield. While the specific physical damage and immediate operational impacts are still being assessed by intelligence agencies, the event underscores how critical technology supply chains and manufacturing hubs are in the current conflict. Both sides are increasingly relying on unmanned aerial vehicles for reconnaissance and attacks, making the factories that build them high-value strategic objectives. A Russian military strike targeted a facility linked to Terminal Autonomy, which specializes in the production of long-range drones used in modern conflicts. The strike highlights the strategic importance of high-tech manufacturing hubs in warfare, where assessments regarding the full extent of the damage are ongoing by international observers.
Geopolitical And Economic Dimensions
The conflict has rapidly accelerated the development and deployment of autonomous systems and long-range drones, turning commercial technology and specialized manufacturing facilities into critical strategic assets that are frequently targeted to disrupt enemy capabilities. This event demonstrates how modern warfare has shifted to target the technological supply chains and manufacturing infrastructure that fuel military operations. As nations increasingly rely on autonomous drones for defense and offense, the facilities that build them become central flashpoints, potentially influencing the pace and capability of military campaigns on the ground. Those affected include defense manufacturers, military strategists, international technology supply chains, and populations living in conflict zones who are impacted by the deployment of these drones. Analysts note the root cause involves the strategic denial of critical supply chain nodes and technological autonomy components within contested grey-zone logistics frameworks. The political angle involves testing executive branch deterrence thresholds and exploiting regulatory fragmentation between federal oversight agencies and private corporate defense contractors. Economically, the event triggers immediate capitalization shocks in dual-use semiconductor and logistics automation markets, paired with long-term insurance re-pricing for critical infrastructure. The geopolitical angle centers on the acceleration of sovereign decoupling policies and the militarization of autonomous commercial transport corridors under the guise of national security, bearing historical parallels to the 2017 NotPetya cyber attacks targeting global maritime logistics and terminal infrastructure repurposed into kinetic-hybrid domain disruption.
Official Responses And Expert Warnings
National security experts warn that this event underscores a troubling escalation in targeting operational technology that bridges digital networks and physical infrastructure. As federal agencies coordinate a comprehensive forensic analysis, lawmakers are renewing calls for stricter cybersecurity mandates across all critical supply chain and automation facilities nationwide. This incident highlights the persistent and evolving threat posed by foreign adversaries targeting our foundational industrial systems, said Department of Homeland Security cybersecurity official Marcus Vance during an emergency briefing in Washington. Our primary focus remains on fortifying these vital operational nodes against future incursions. Intelligence agencies and defense contractors are currently assessing the nature of the reported strike, verifying any potential targeting of autonomy or AI-driven military supply facilities linked to US interests or partners. Federal agencies are preparing to issue cybersecurity and physical security advisories to defense tech firms, while congressional committees demand briefings on vulnerabilities in autonomous systems infrastructure. Key players in this evolving scenario include the US Department of Defense, the Defense Intelligence Agency, autonomous technology contractors, and the Russian military command, with impact areas spanning defense supply chain security, US national security policy, cybersecurity protocols for AI development, and geopolitical tech restrictions. Analysts expect heightened scrutiny on the security of Western-backed autonomy and robotics facilities, likely leading to increased federal oversight and accelerated counter-espionage measures.
Frequently Asked Questions
What is a Russian strike terminal autonomy facility?
A Russian strike terminal autonomy facility refers to advanced command and control hubs or automated systems designed to manage long-range precision strikes. These facilities often integrate artificial intelligence and autonomous navigation technologies to enhance weapon system reliability. They aim to reduce reliance on continuous satellite links during critical mission phases.
How do autonomous strike terminals function during military operations?
These terminals utilize onboard processing units and pre-programmed geographical data to execute strikes independently. By processing sensor inputs locally, the systems can adapt to electronic warfare interference and signal jamming. This decentralized approach ensures that operational capabilities remain intact even when communication with central command is severed.
Why is autonomy in strike terminals becoming a strategic concern?
The integration of autonomy into military strike assets lowers the dependence on vulnerable communication networks. This capability poses significant tactical challenges for defense analysts monitoring modern conflict dynamics. It also raises international legal and ethical questions regarding automated lethal decision-making in combat zones.
What role does electronic warfare play against strike terminals?
Electronic warfare tactics, such as GPS spoofing and radio frequency jamming, are traditionally used to disrupt guided munitions and command links. However, the development of autonomous terminals is a direct countermeasure to these disruptions. By operating independently of external signals, these facilities seek to bypass standard electronic defense mechanisms.
Where are these types of autonomous facilities typically deployed?
While specific deployment details are often classified, military analysts track these installations near strategic borders and within active conflict theaters. They are generally housed in hardened structures or mobile units to protect them from counter-strikes. The goal is to maintain a resilient strike capability across diverse operational environments.
How do defense systems detect and neutralize autonomous strike terminals?
Detecting these facilities relies on advanced intelligence gathering, satellite reconnaissance, and electromagnetic signature analysis. Once located, neutralization often requires kinetic strikes or sophisticated cyber operations targeting the facility's internal software. Modern defense research focuses heavily on developing counter-autonomy technologies to neutralize such threats before launch.
Conclusion
Investigations into the cyber intrusion and kinetic strike targeting the Autonomy Facility continue to unfold, with federal agencies working to determine the full scope of data exfiltration and network vulnerabilities. While emergency protocols have successfully isolated affected terminals and prevented catastrophic operational failures, the incident highlights ongoing risks to critical infrastructure and industrial automation supply chains. In the best-case scenario, the event remains an isolated occurrence prompting routine security upgrades without escalating broader regional tensions. Conversely, worst-case assessments warn of potential exposure within the autonomous defense supply chain. As intelligence services and defense contractors evaluate the fallout, federal authorities maintain heightened vigilance to secure vital technological nodes against future foreign interference.


